
All projects
Case Study
ISO/IEC 27001 Advisory
Consulting and internal audit support for an Information Security Management System (ISMS) based on ISO/IEC 27001 as the governance framework.
- Client
- Lembaga Filantropi Nasional
- Industry
- Information Security
- Category
- Cybersecurity
- Year
- 2025
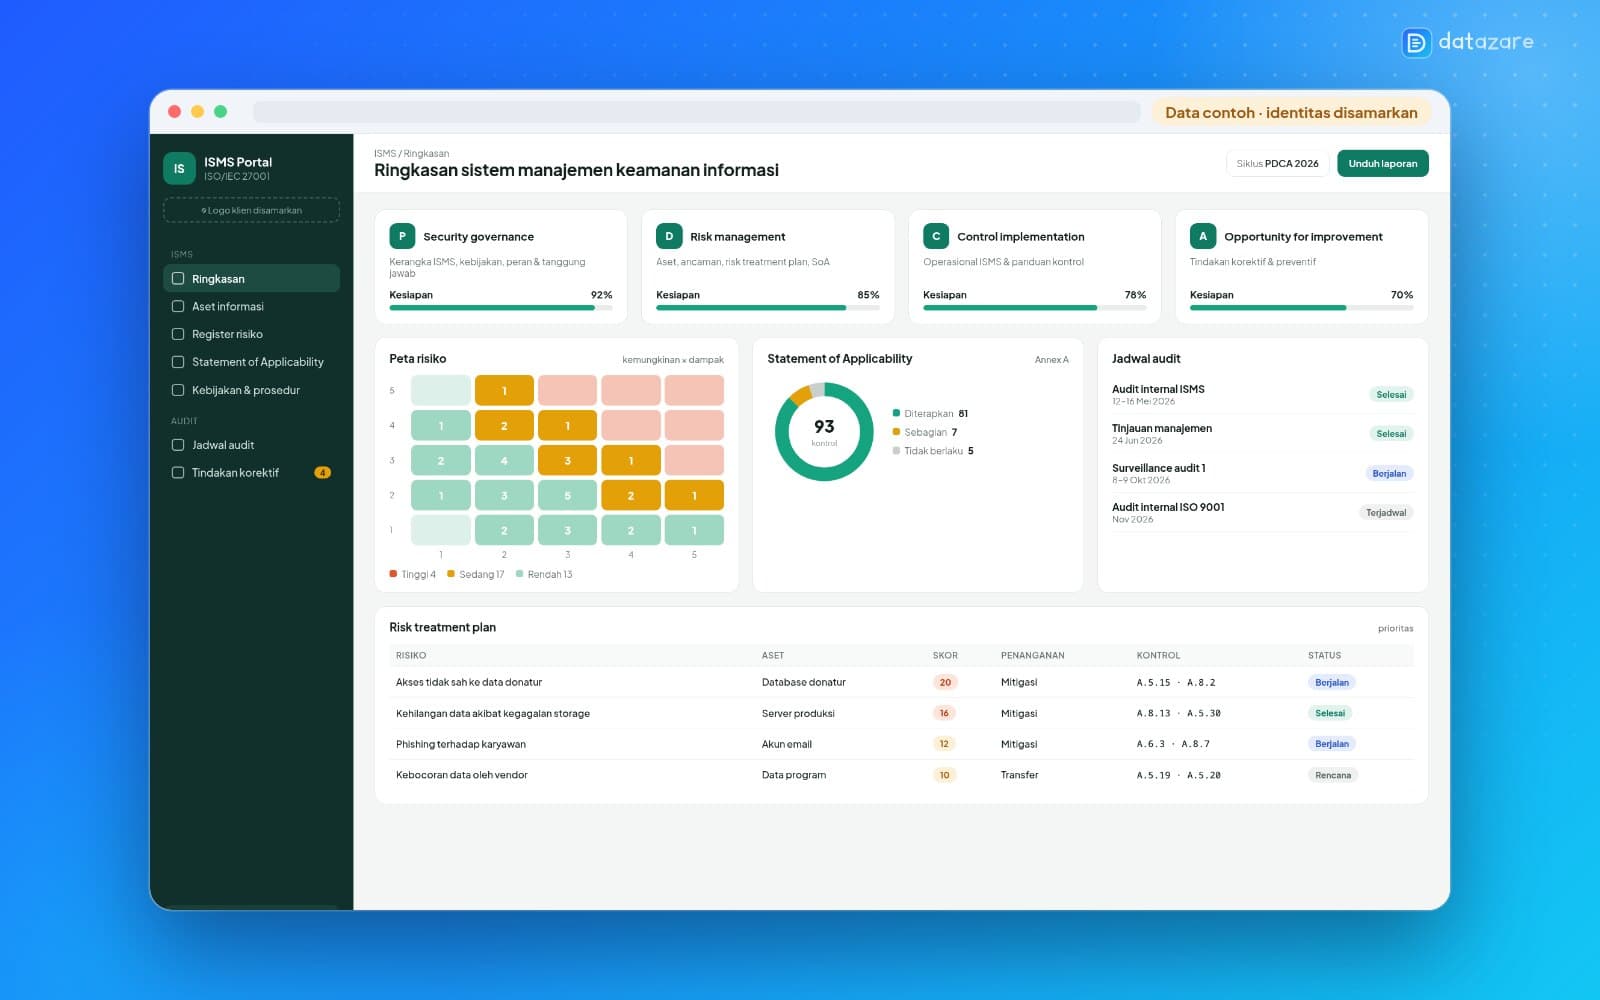
ISO 27001 & 9001
Standards supported
4
ISMS pillars
PDCA
Improvement cycle
Challenge
The organization needed to align business goals (compliance, donor trust, growth) with documented, auditable information security controls.
Solution
We supported the ISMS implementation using the Plan-Do-Check-Act cycle across four pillars:
- Security Governance — ISMS framework, policies, roles & responsibilities
- Risk Management — asset inventory, threat identification, risk treatment plan, Statement of Applicability
- Control Implementation — ISMS operations & control guidelines
- Opportunity for Improvement — continuous corrective & preventive actions
Other projects
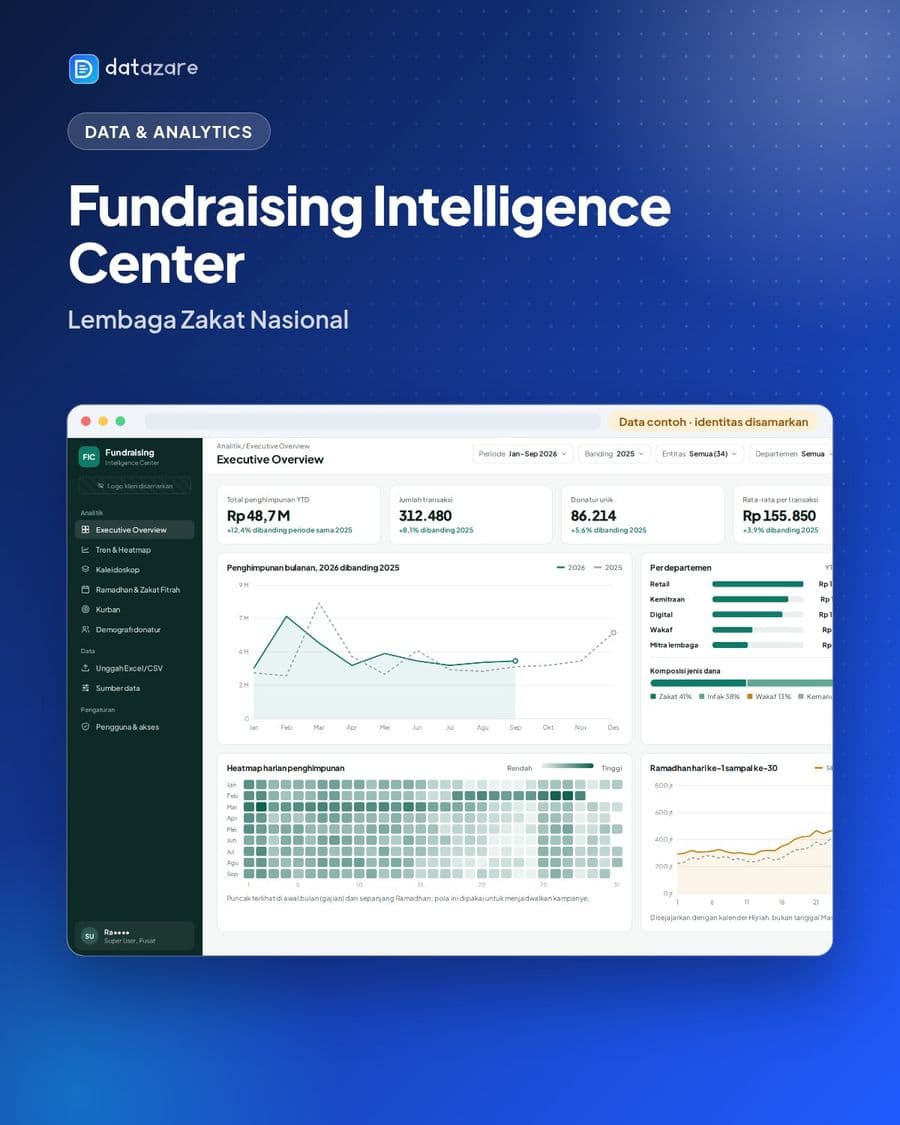 Data & Analytics
Fundraising Intelligence Center
Lembaga Zakat Nasional · Fundraising Analytics
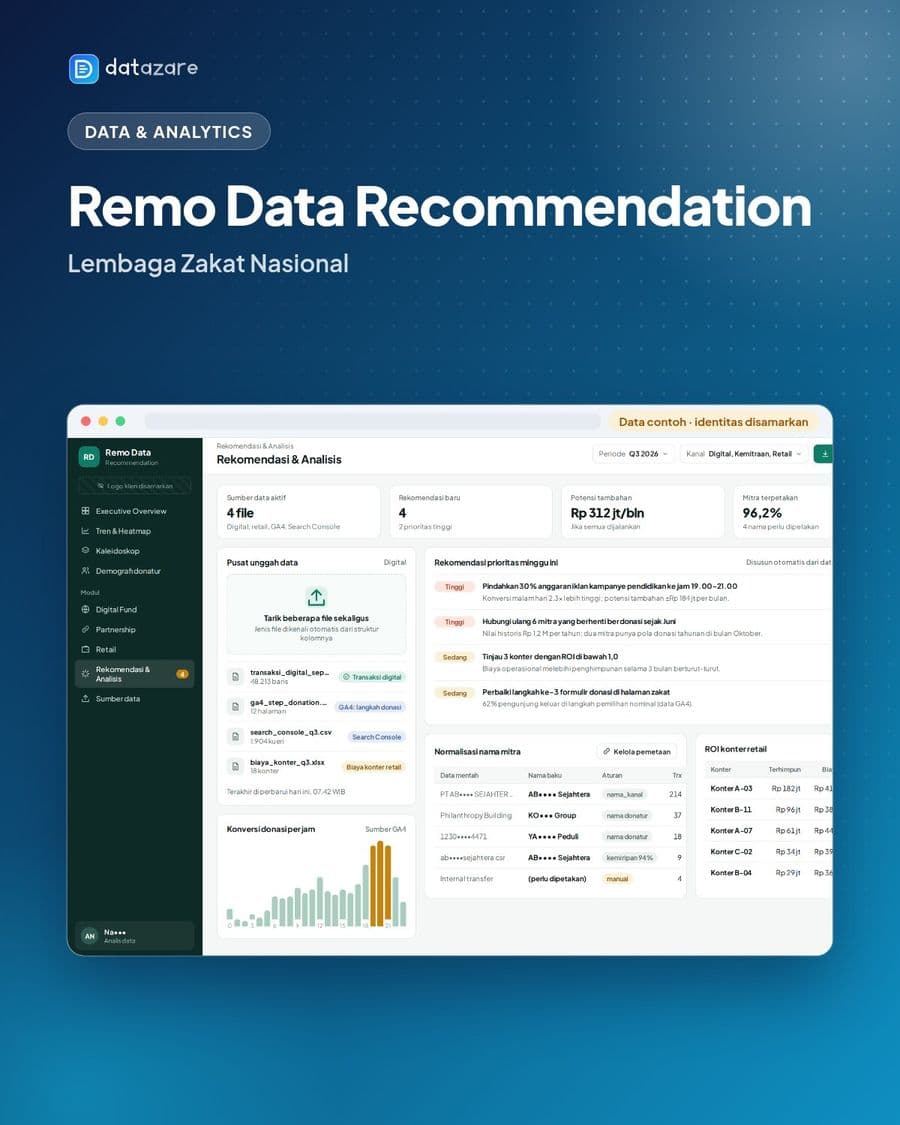 Data & Analytics
Remo Data Recommendation
Lembaga Zakat Nasional · Digital Donation Analytics
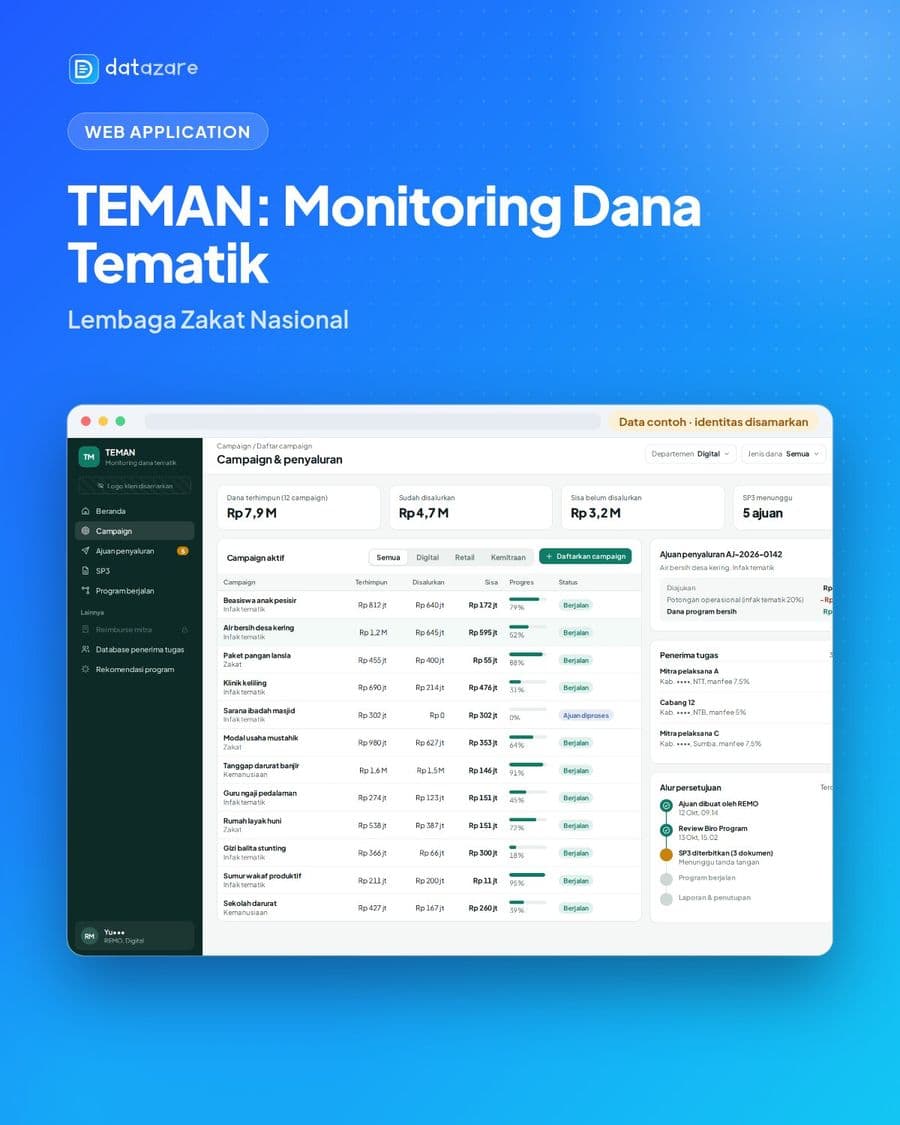 Web Application
TEMAN: Thematic Monitoring & Allocation Network
Lembaga Zakat Nasional · Program Distribution
 Web Application
Himpun: Donation Entry App
Lembaga Zakat Nasional · Donation Operations
Facing a similar challenge?
Tell us what you need — we will help you design the solution.