
Vulnerability Assessment & Penetration Testing
Comprehensive security testing for web, API, and mobile applications: automated vulnerability scanning followed by manual penetration testing, CVSS-based reporting, and fix retesting.
- Client
- Lembaga Filantropi Nasional
- Industry
- Application Security
- Category
- Cybersecurity
- Year
- 2026
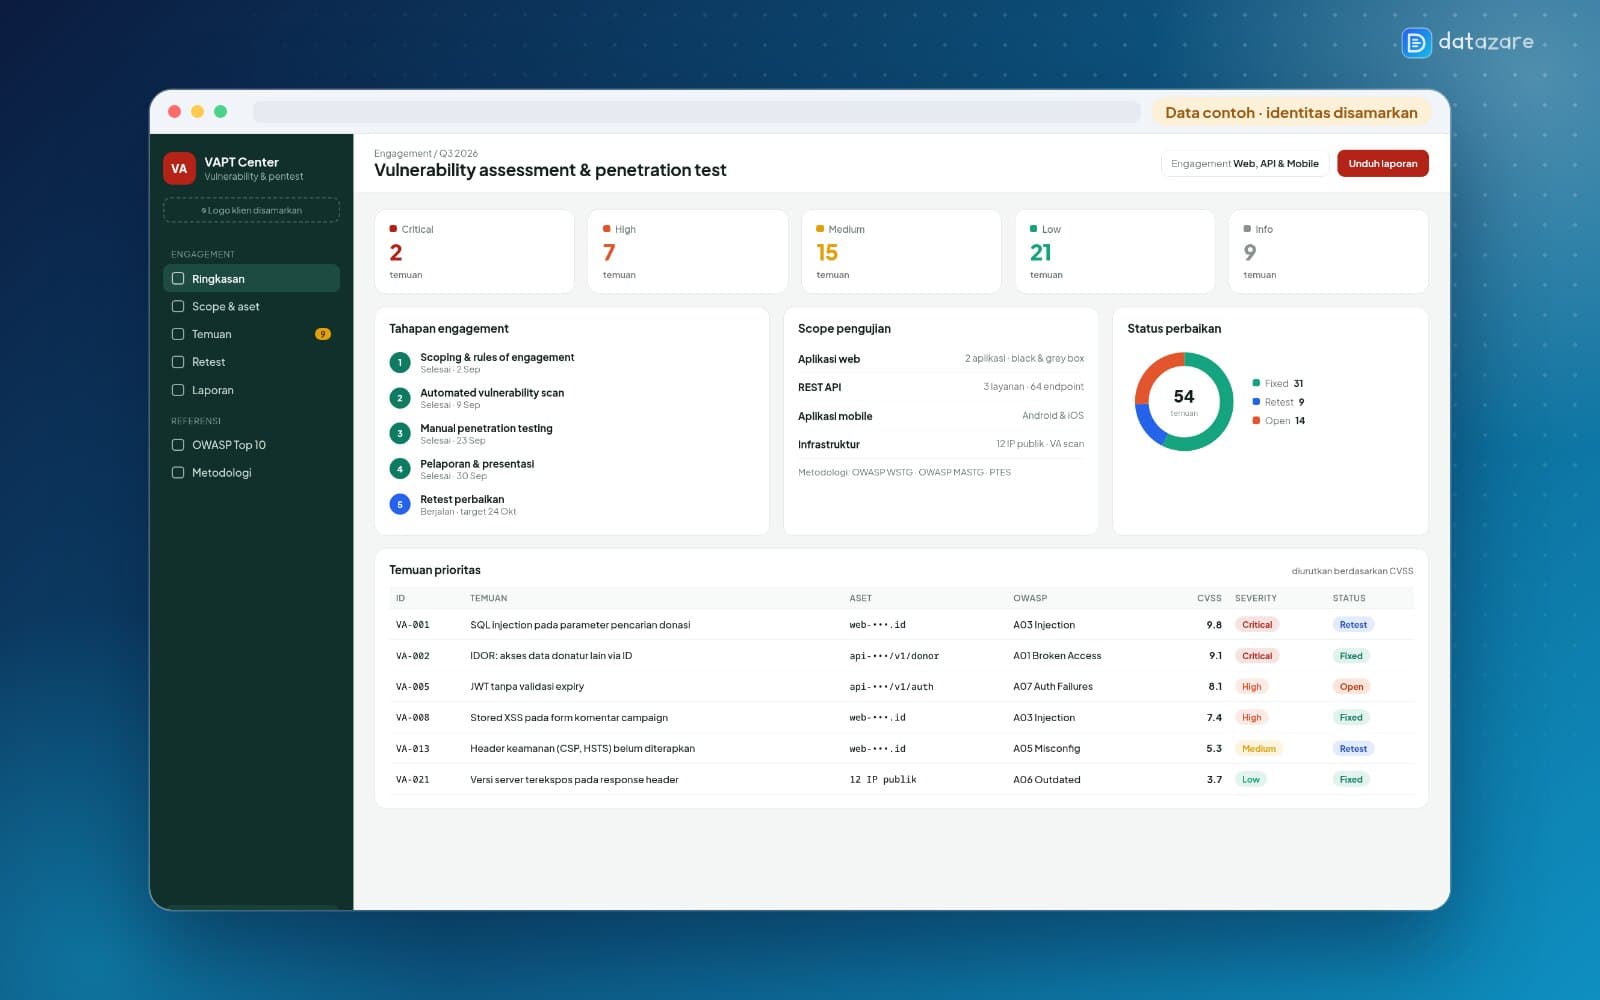
Web · API · Mobile · Infra
Scope
OWASP WSTG · MASTG · PTES
Standards
CVSS + OWASP Top 10
Risk scoring
Challenge
Donation applications and APIs holding donor data had to be proven secure before and after release, while also meeting information security audit requirements.
- No regular independent security testing
- Previous findings weren’t tracked until fully fixed
- Developers needed clear, prioritized remediation guidance
Solution
We ran a phased VAPT engagement: scoping & rules of engagement, automated vulnerability scanning, manual penetration testing (black & grey box) following OWASP WSTG, OWASP MASTG, and PTES, then reporting and retesting.
- Every finding is mapped to the OWASP Top 10 and scored with CVSS
- Technical remediation guidance per finding, prioritized by risk
- A remediation status dashboard (open, retest, fixed) and retesting until resolved
All figures, names, and identities in the screenshots are sample data; client logos and personal data are masked.
Gallery
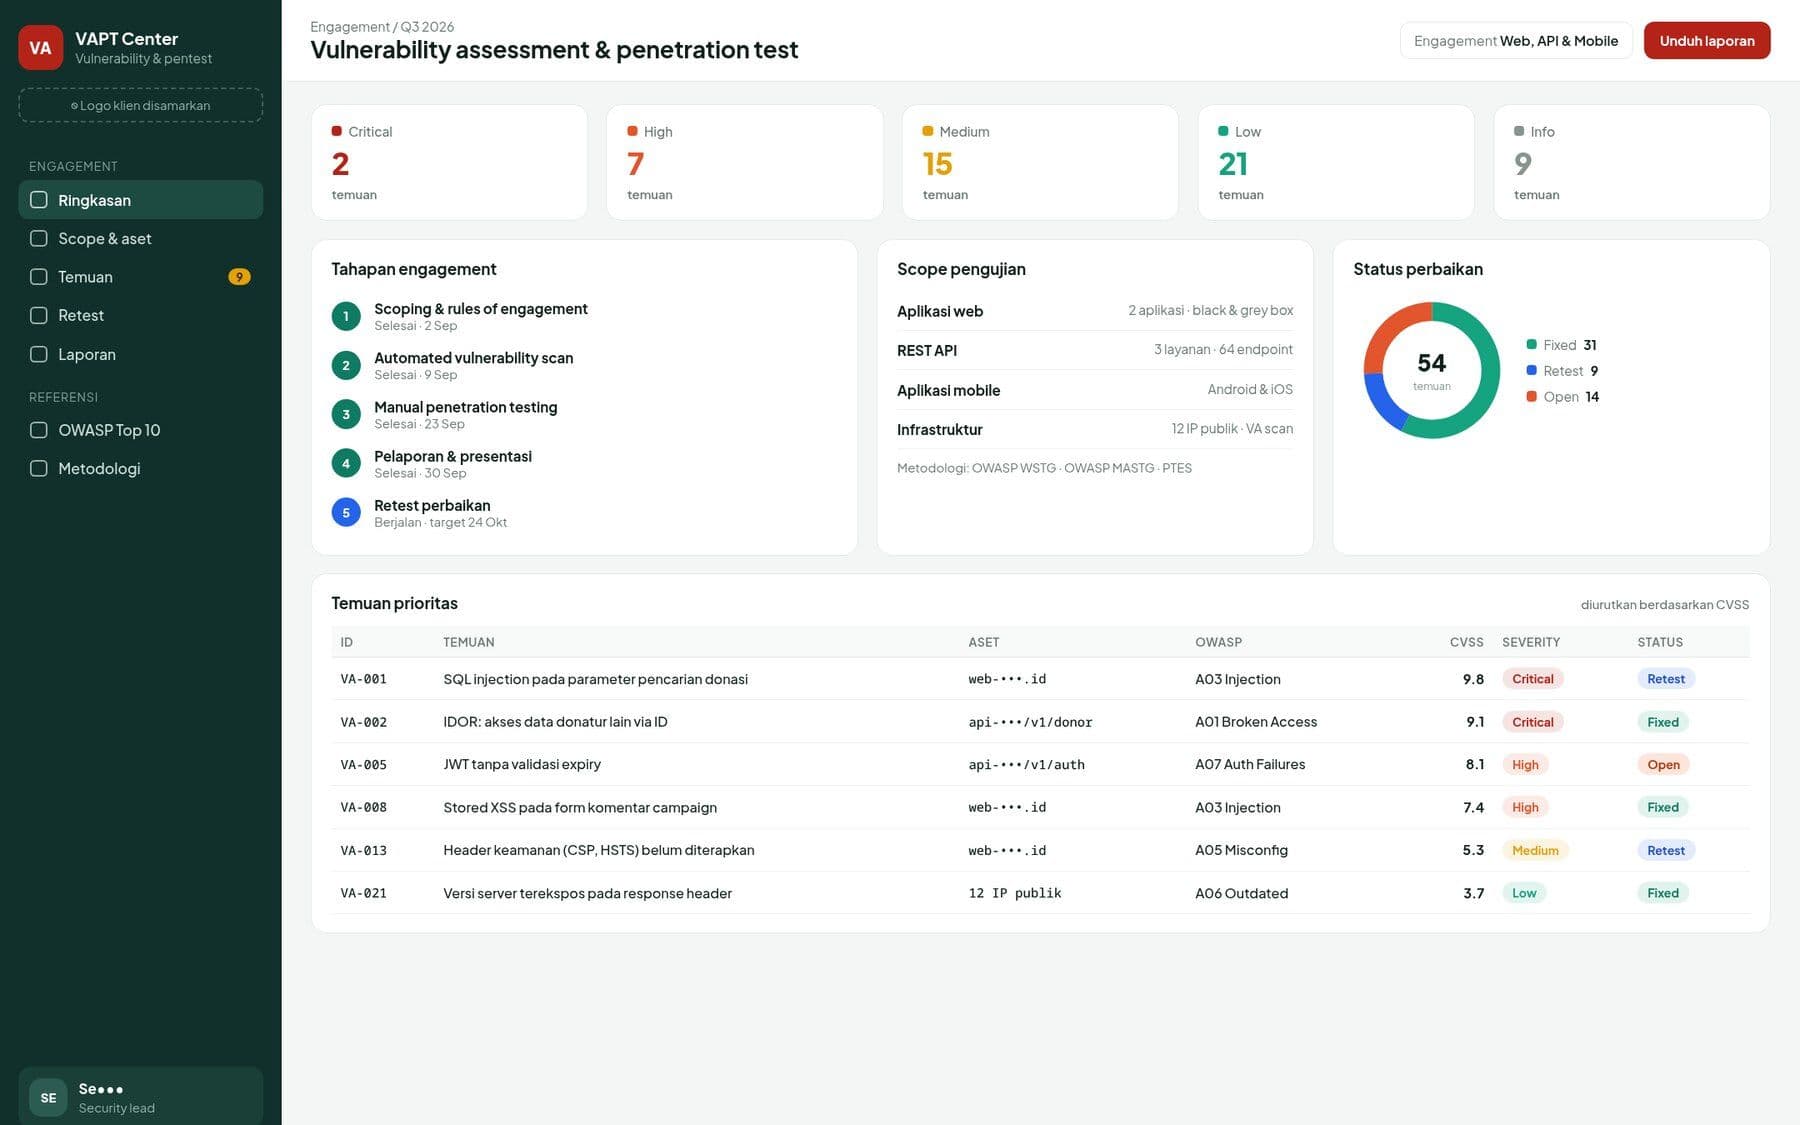
VAPT engagement dashboard
Other projects
 Data & Analytics
Fundraising Intelligence Center
Lembaga Zakat Nasional · Fundraising Analytics
 Data & Analytics
Remo Data Recommendation
Lembaga Zakat Nasional · Digital Donation Analytics
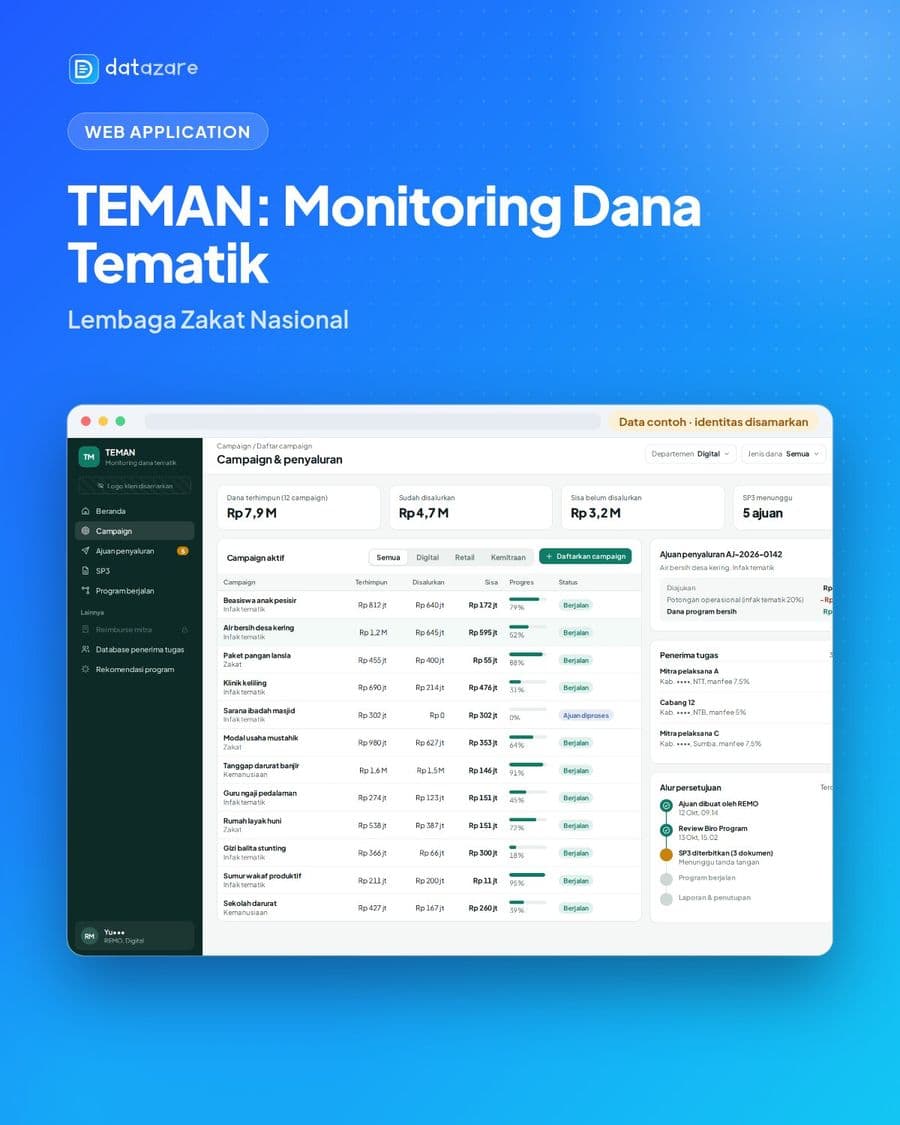 Web Application
TEMAN: Thematic Monitoring & Allocation Network
Lembaga Zakat Nasional · Program Distribution
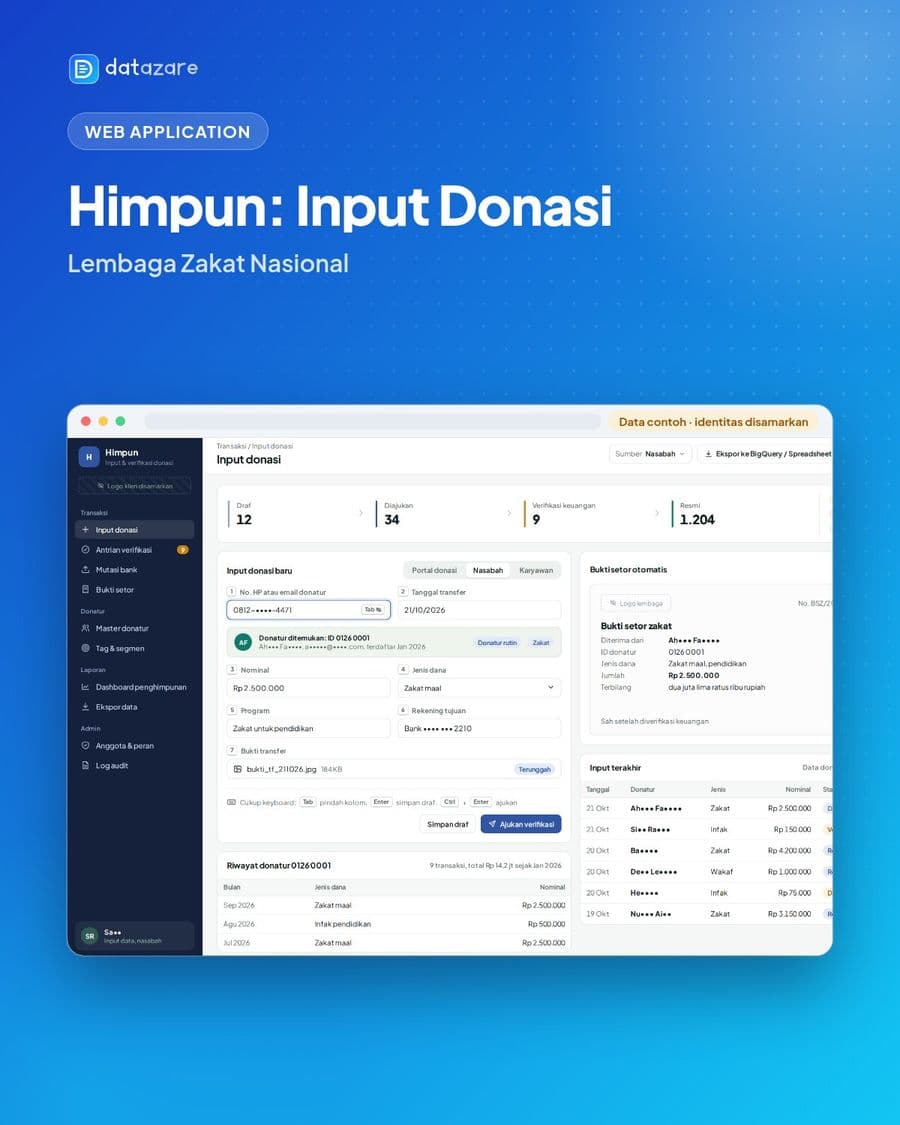 Web Application
Himpun: Donation Entry App
Lembaga Zakat Nasional · Donation Operations
Facing a similar challenge?
Tell us what you need — we will help you design the solution.